AI Penetration Testing + Attack Surface Management AI automation · Expert validation Attack path validation · Exposure risk management

AI Penetration Testing and Attack Surface Management

Use AI penetration testing to verify what attackers could actually exploit.
Find the websites and servers you expose to the internet, and track their risks and fixes.

  • Attack scenarios validated by AI and experts
  • Discovery of external assets and brand threats
  • Fix priorities and retest

ASM (Attack Surface Management): finding and managing the points an outside attacker could target

AI Red Team Top Excellence Award · team member Vulnerabilities reported to Korea's KVE 10 years in security
OWASP Top 10:2025 NDA signed before testing
Services

Choose a service
by what you need to check

Results as shown in the actual product

Risks, owners and fix status
managed in one place
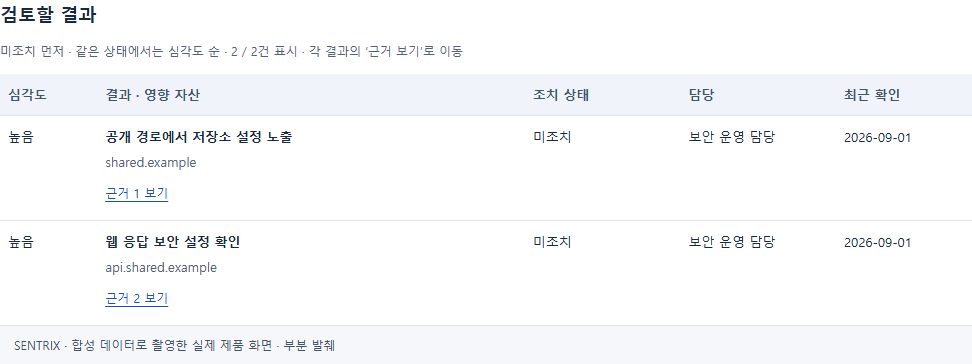
ASM report screen from the product (Korean interface), showing risk level, affected assets, owners and fix status
Actual product screen (Korean interface) built with synthetic data.
See the screen and deliverables in detail →
01What you receive

Evidence you can report.
Fixes you can apply right away.

Deliverables for internal reporting and for your developers' fixes. The exact items depend on the contract scope.

Illustrative sample A sample report built on a fictional scenario. It is not based on any real customer's results, and deliverables depend on the contract scope.

SAMPLE / Decision summary

The risks to fix first, at a glance

SituationBefore launching a customer-facing web service

Checking access rights for regular users and administrators

Business impactOther customers' data could be exposed

Data access boundaries between accounts need checking

Example fix priorityFix before launch

Strengthen permission checks, then retest

The person in charge sees the business impact and priorities and can use them in internal reports.

SAMPLE / Developer fix guide

From evidence to the fix

  1. 01 · Test condition

    Compare the data each authorized test account, A and B, can access

  2. 02 · Evidence

    Record that account A can view account B's test data

  3. 03 · Fix direction

    Check on the server whether the requester may access the data owner's records

  4. 04 · Done when

    Unauthorized access is blocked and normal user functions still work

Developers see the evidence, the fix direction and the completion criteria together.

SAMPLE / Retest results

What is fixed and what remains

Before fix
Example findingAnother account's test data is accessible
After fix
Example verificationAccess to other accounts' data is blocked
Normal functions
Example function checkUsers can still view their own data
Remaining items
Example follow-upAPIs outside this scope are agreed separately

An illustrative example of the flow: after the customer's developers or operators make the fix, SENTRIX rechecks it within the agreed scope. This is not a real customer case or test record.

A summary of the external exposure risks of a URL you enter

Request a one-page risk summary
02How it works

From scope agreement
to assessment and fix verification

01 / 04
Scope

Scope and schedule

We confirm the targets and goals, then propose cost, schedule and deliverables. Work starts after testing authorization and an NDA are in place.
→
02 / 04
Assess
Assessment
AI automation combined with manual testing to find vulnerabilities from a real attacker's point of view.
→
03 / 04
Report
Report / guide
A report with the vulnerabilities found, their risk levels and specific fixes.
→
04 / 04
Monitor
Retest and ongoing operations
We re-verify your fixes within the contract scope. Device operation and monitoring are agreed separately if needed.

Testing starts after a non-disclosure agreement (NDA) is signed and follows the agreed targets, permissions and time windows. We keep access to sensitive data to a minimum and agree on how assessment data is delivered, stored and destroyed when we sign the contract.

03Track record

Verified credentials
and track record

Awards and competitions

Competition
2025 AI Red Team Challenge hosted by Korea's Ministry of Food and Drug Safety (MFDS), Top Excellence AwardAchievement of a team member
Award
Competition
Korea Transportation Safety Authority Security Challenge, Encouragement Award
Award
Competition entry
Cybersecurity Challenge, IoT track finals
Teaching
Hands-on security lecturesKyonggi University and others
Education

Vulnerability reports & standards

KVE
Vulnerabilities reported to Korea's national database (KVE)Including KVE-2024-0142 (authentication bypass)
Reported
ISMS-P
Certification consulting · audit supportFor ISMS-P (Korea's information security and personal information management certification): gap analysis, technical assessment, evidence collection and audit support
Advisory
OWASP
Assessment framework based on the Top 10:2025All items mapped · executive summary included
Standard
Public sector
Registered supplier on KONEPS (Korea's public procurement service)Can respond to quote and proposal requests from public institutions
Registered

Competition, teaching and vulnerability-report history. Mentioning an organization does not imply a partnership, sponsorship or customer relationship with it. Download the company profile (PDF, Korean)

Our team and resources

Our experts' verified credentials and material for your internal review

About us and our track record →
04FAQ

Key questions
before you start

How does AI penetration testing differ from Attack Surface Management (ASM)?
SENTRIX ASM checks your external assets, how they connect, brand impersonation and look-alike domains, and sets fix priorities for the whole organization. AI penetration testing combines AI automation with expert validation to verify what can actually be exploited after login, such as permissions, payment flows and business logic, within the accounts and scope we agree on. See the ASM scope and the AI penetration testing scope.
What should I prepare for a quote?
The targets (web, API, app and so on), the purpose of the assessment and your preferred schedule. We refine the scope based on the number of targets and your account and permission structure. If your budget or detailed scope is not set yet, we can start from your current situation. Contact Us
Can you test a service that is already live?
Yes, live services can be tested. We agree in advance on written authorization, testing time windows, allowed tests and stop conditions. Items that could affect operations are moved to a separate test environment or a limited scope.
How do retests and device operations work?
The number and period of retests depend on the assessment package. Targets and cycles for device deployment, policy changes and ongoing monitoring are agreed separately. If you only need your existing devices operated, you can also discuss the operating scope with us.
Contact

Assessment scope and follow-up
matched to your security challenge

Tell us the targets, the purpose of the assessment and your preferred schedule.
You can contact us before the scope or budget is set. We reply within one business day.

For your review, you can request a one-page risk summary. Public institutions can request an assessment or a quote for their institution. We reply within one business day and explain the contracting steps and the quote and proposal documents your institution needs.

Email
We reply within one business day · [URGENT] Incident response
Location
Suji-gu, Yongin-si, Gyeonggi-do, South Korea
Meetings by appointment
Business hours
Mon–Fri · 10:00–19:00 KST
For incident response, put [URGENT] in the subject line and we check it first on business days.